Risk is one discipline. We treat it that way.
A practitioner-led, veteran-owned firm that governs cyber, physical, and human capital risk as a single discipline.
No figureheads. No stock imagery. Our people are measured by what they have built: resumes, credentials, results.
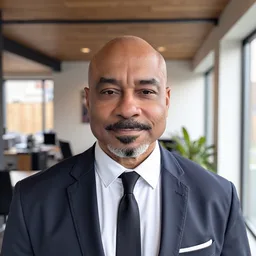
M.K. Palmore has led security across three arenas most people only ever see one of. He began in uniform: a graduate of the U.S. Naval Academy, commissioned as an officer in the United States Marine Corps, where leadership is proven under pressure rather than on paper.
He carried that standard into federal service, rising to senior executive rank at the FBI. He then moved into the private sector, holding security leadership roles at Palo Alto Networks and Google Cloud, translating the operator's discipline into the language of the boardroom.
Apogee exists because that range is rare and buyers need it whole: cyber, physical, and human risk, governed by someone who has answered for all three. A CISSP, he built the firm to put that judgment within reach of organizations that cannot hire it in-house.
"We run every engagement the way we ran missions, with discipline, ownership, and a standard we don't lower."
M.K. Palmore in the broader conversation on risk.
Advisory Board Seats
- 01Island.io: Advisor
- 02Dataminr: Public Sector Advisory Board member
- 03Marines' Memorial Association: Member, Board of Directors
Podcast Properties
- 01The Risk Apogee: a practitioner-focused show examining enterprise risk, cyber threats, and leadership under pressure.
- 02Amplified: The Leadership Student 2.0: conversations on leadership development, professional growth, and the mindset required to lead through complexity.
Senior counsel, on call.
Senior counsel from across government, technology, and law: the kind of experience our clients draw on before they need it.
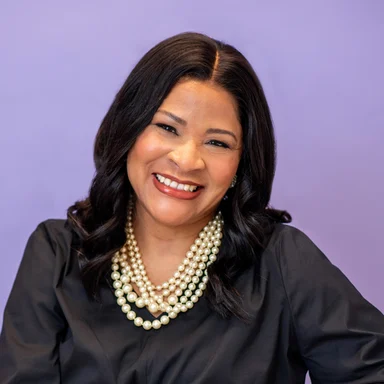
Principal Advisors and practice leads.
Each has held the decision they now advise on, and each answers by name for the outcomes in their domain.
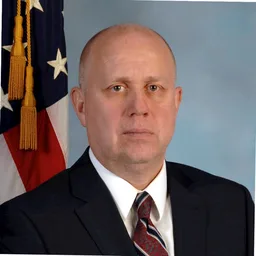
Former FBI senior executive and 34-year Bureau intelligence veteran specializing in intelligence analysis and analytic tradecraft; leads the Rogue Risk Analysis Group.
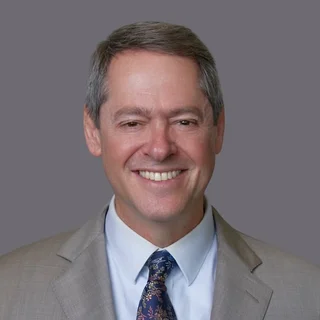
Public Safety Leader and Advisor with over three decades on the front lines of Bay Area law enforcement and emergency services, including 25 years with the City of Mountain View, where he served as Police Chief and Interim City Manager.
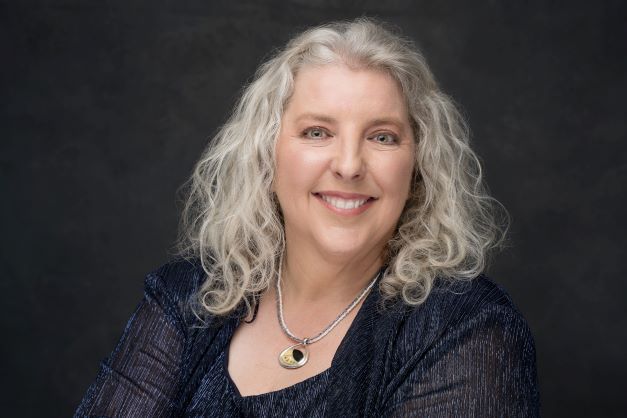
U.S. Air Force veteran and former VP of Security Engineering & Architecture and Interim CISO at TD SYNNEX, with more than 20 years of cyber defense experience.
Former Chief of Police and public sector technology leader with experience as Microsoft's Majors Growth Account Lead for State & Local Government and Education (SLED).
Retired FBI Supervisory Special Agent with Certified Protection Professional (CPP) and Physical Security Professional (PSP) credentials. Enterprise security practitioner.
Firm leadership and operations.
The people who run the firm, so the practitioners can stay on the work.
U.S. Marine Corps veteran and former Verizon management leader with small business ownership expertise; leads business operations and public sector development.
Strategic program leader with more than a decade of experience in stakeholder engagement, brand partnerships, and organizational growth; directs the Apogee Speakers Bureau.
Senior operations program manager with 15 years of client experience leadership; owns client experience and program execution.
Built for organizations where risk carries consequence.
We serve public agencies, critical infrastructure operators, and private organizations for whom a failure in cyber, physical, or human risk produces damage they cannot absorb quietly. Qualification is by consequence, not by company size.
The firm that prepares an organization should not be the firm that grades it.
We assess, remediate, prepare, and govern. We do not attest, certify, or audit a program we built. Remediating what we found is not a conflict. Grading what we built is. We prepare clients for third-party assessment, coach their teams, and sit beside them on assessment day. Somebody else does the assessing.
Our Mission
To help organizations grow with confidence, by governing their risk, strengthening their leadership, and turning exposure into resilience.
Ready to take a unified view of enterprise risk?
A Risk Briefing is forty-five minutes with a senior practitioner. You leave with a straight answer on the fastest path forward, whether or not it runs through us.
Request a Risk Briefing